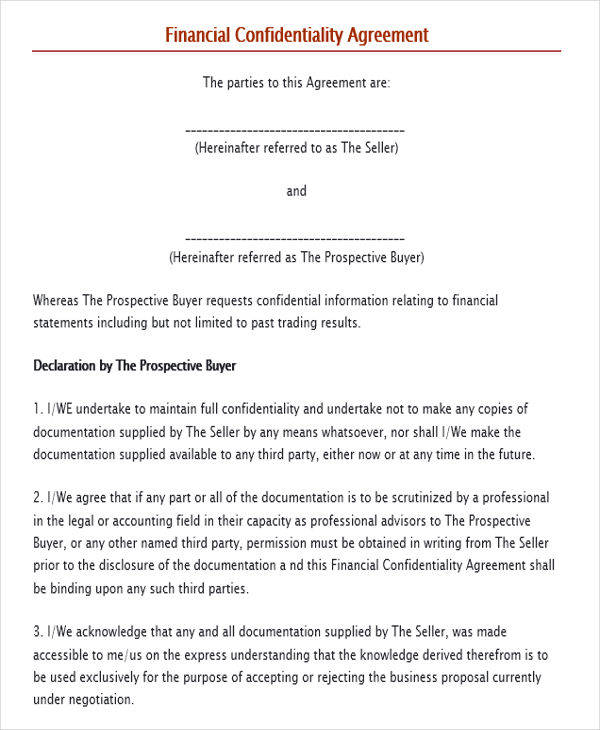
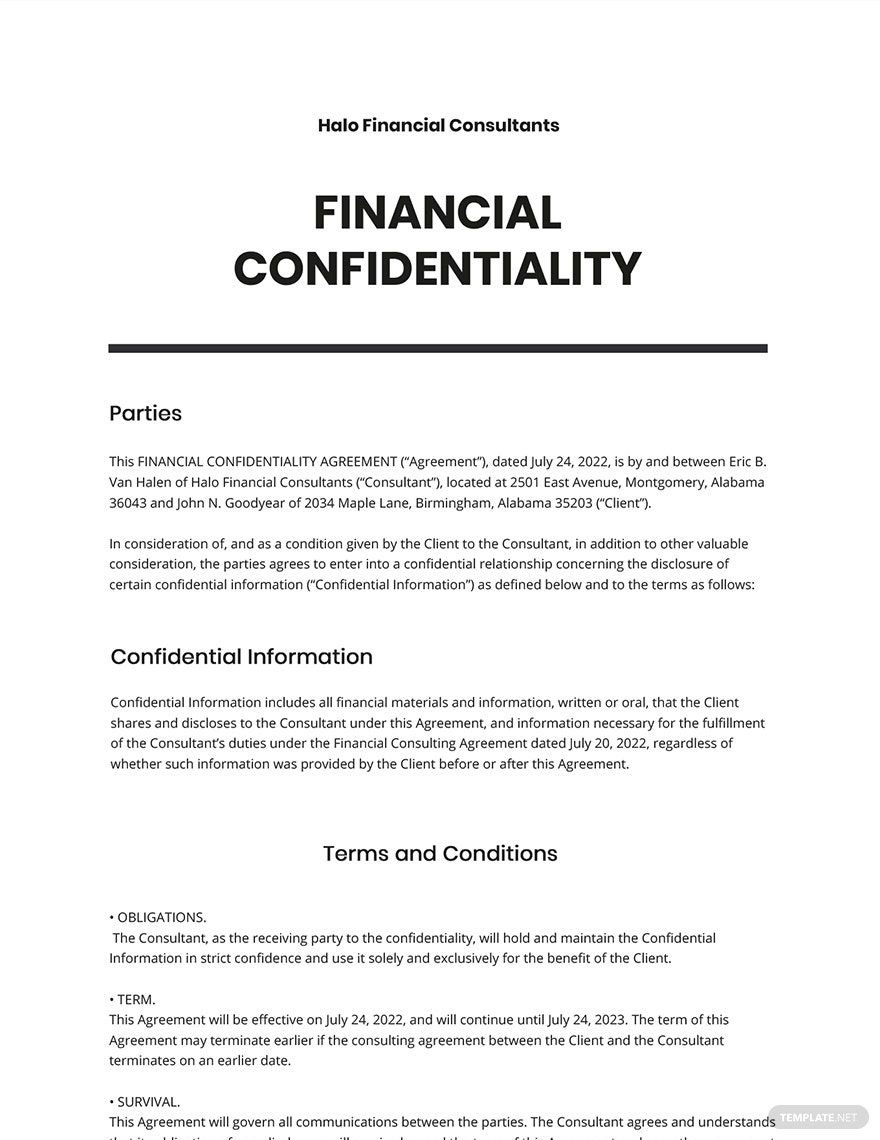
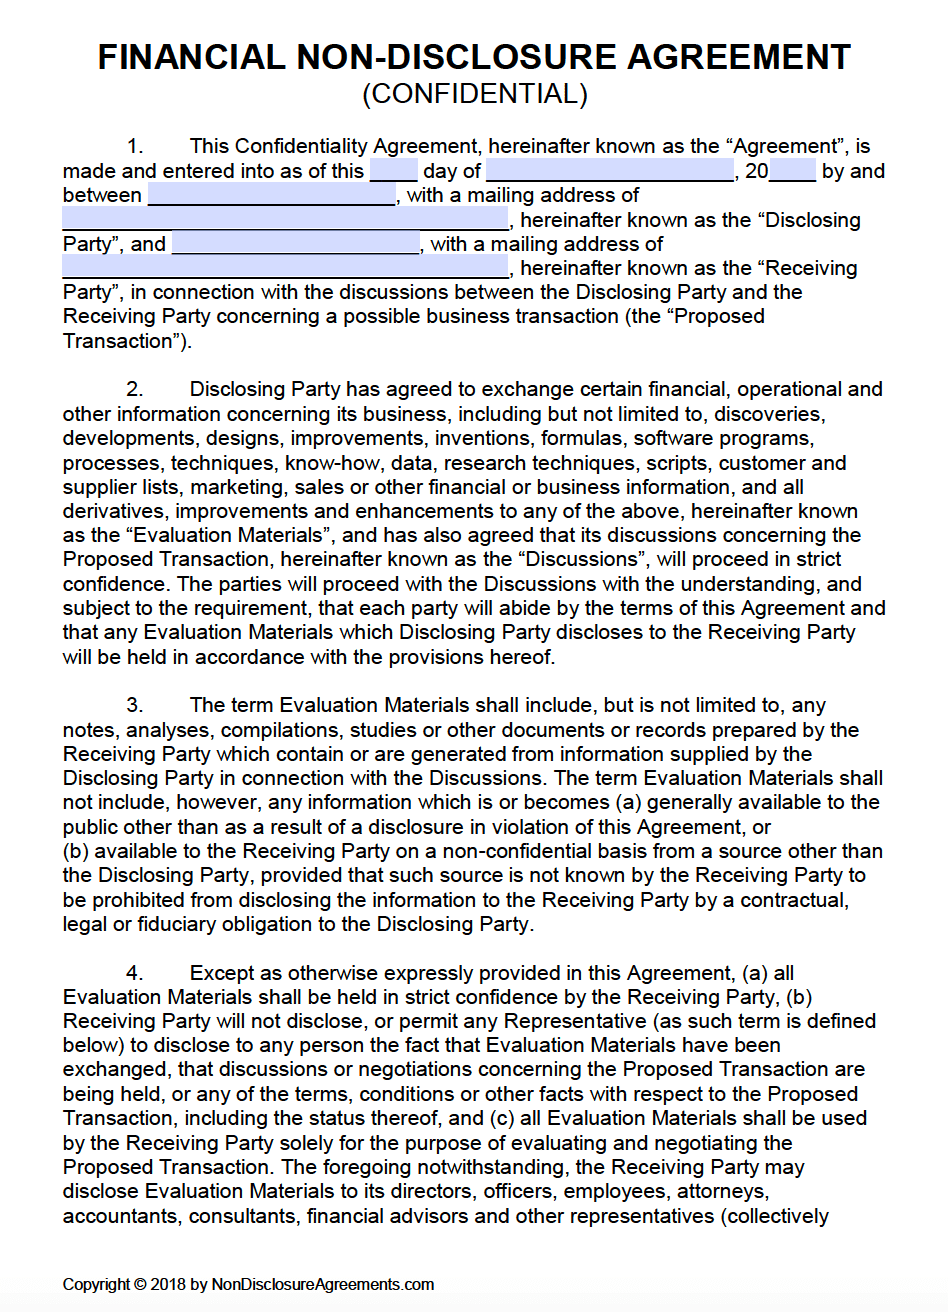
The world of business relies heavily on trust and secure data. Protecting sensitive information – financial records, customer details, proprietary strategies – is paramount. That’s why a robust Financial Confidentiality Agreement (FCA) is increasingly crucial for organizations of all sizes. This article will delve into the essential elements of an FCA, explaining its importance and providing a comprehensive overview of what to include. Understanding and implementing a well-crafted FCA is a proactive step towards safeguarding your business’s valuable assets and maintaining client confidence. Financial Confidentiality Agreement Template – a document that defines the terms and conditions under which information shared between parties is protected. It’s not just a legal formality; it’s a strategic tool for building a sustainable and trustworthy relationship.
The rise of data breaches and cybersecurity threats has dramatically increased the need for legally sound agreements. Companies are facing mounting pressure to protect customer data and maintain compliance with regulations like GDPR and CCPA. A poorly drafted FCA can expose your organization to significant legal and financial risks. Conversely, a comprehensive and well-executed FCA demonstrates a commitment to responsible data handling and fosters a culture of trust. It’s a vital component of a modern business strategy.
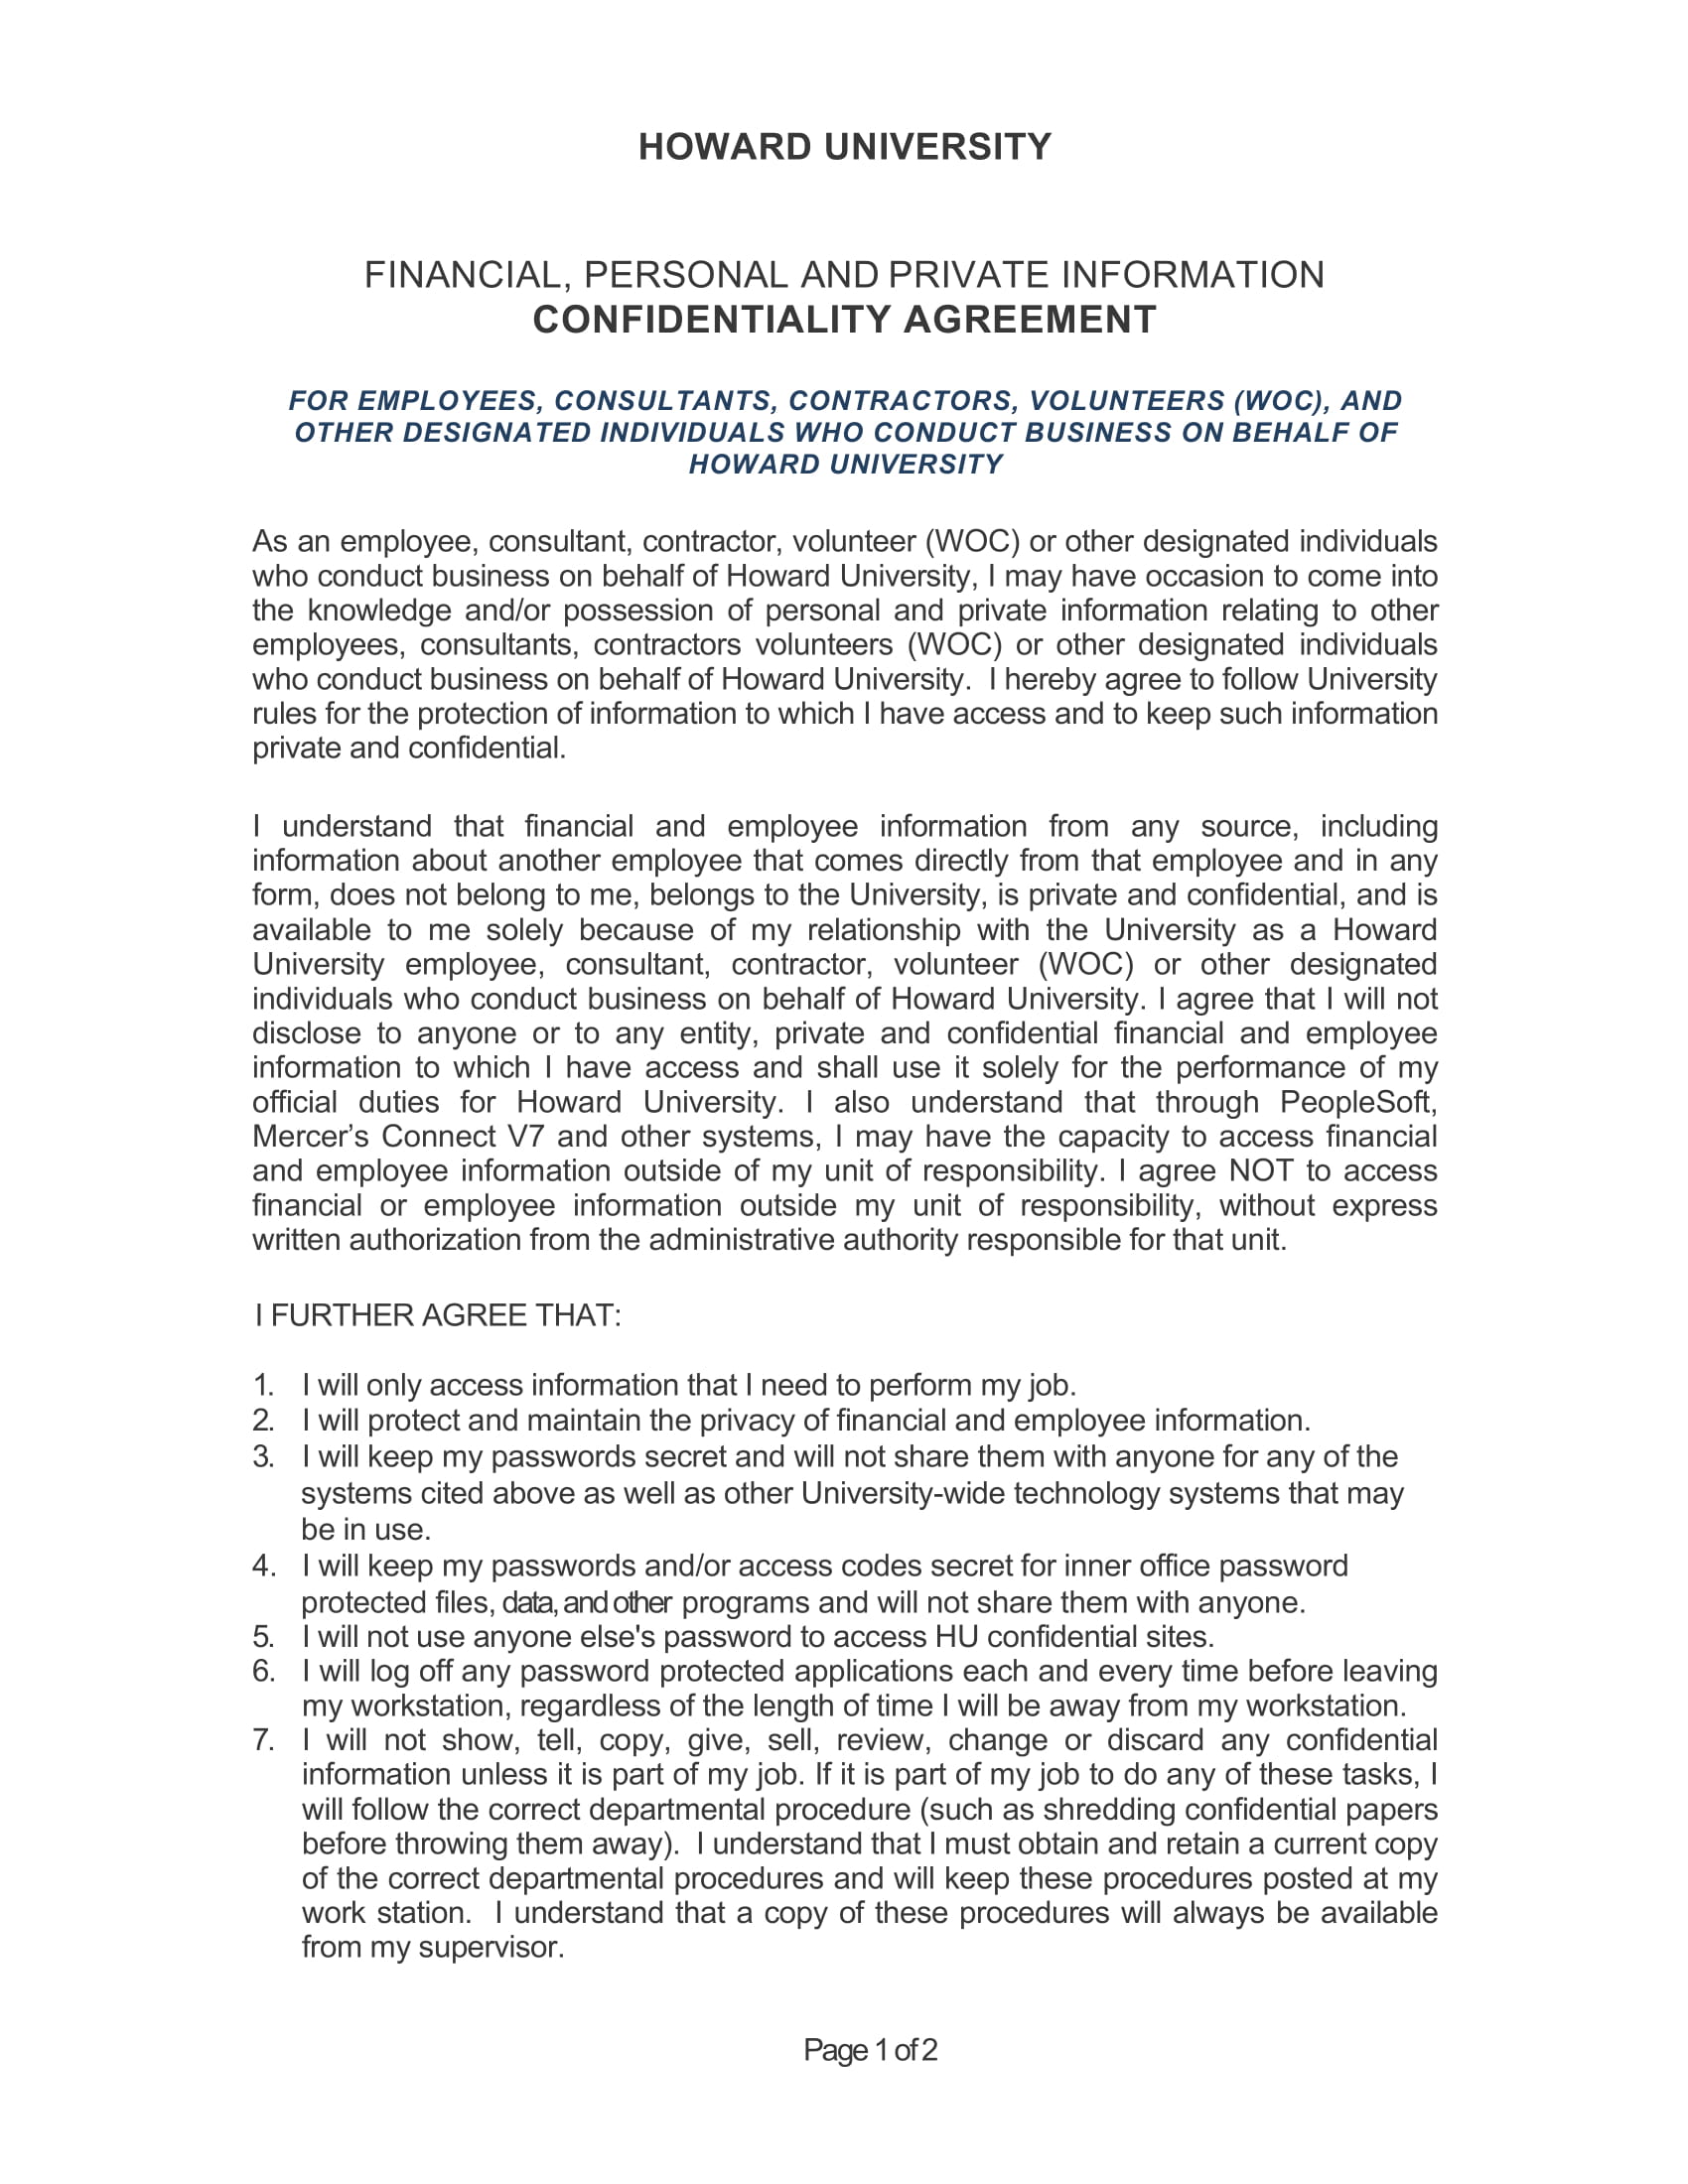
Understanding the Purpose of a Financial Confidentiality Agreement
A Financial Confidentiality Agreement (FCA) is a legally binding contract that outlines the permitted uses and disclosures of confidential information. It’s designed to protect sensitive data from unauthorized access, use, or disclosure. It’s not simply a boilerplate document; it’s a tailored agreement that addresses the specific needs and risks of each relationship. The primary goals of an FCA are to:
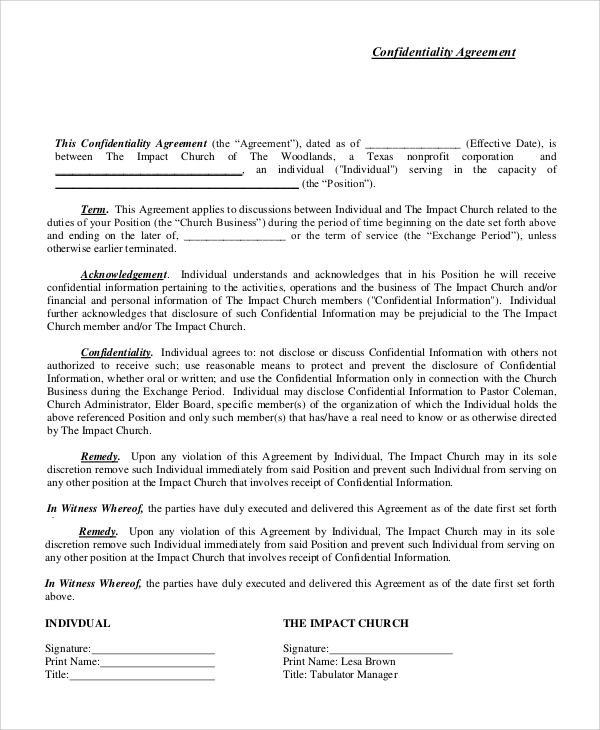
- Define Confidential Information: Clearly identify what constitutes confidential information – this could include financial data, customer lists, trade secrets, marketing strategies, and more.
- Specify Permitted Uses: Outline how the receiving party can use the confidential information. Restrictions on use are crucial.
- Establish Data Security Measures: Require the receiving party to implement reasonable security measures to protect the information.
- Outline Data Retention Policies: Specify how long the receiving party is permitted to retain the information.
- Address Breach Notification: Establish procedures for reporting a breach of confidentiality.
- Clarify Ownership and Liability: Define who owns the information and who is liable for any breaches.
Key Components of a Financial Confidentiality Agreement
A robust FCA typically includes several key sections. Let’s examine some of the most important elements:
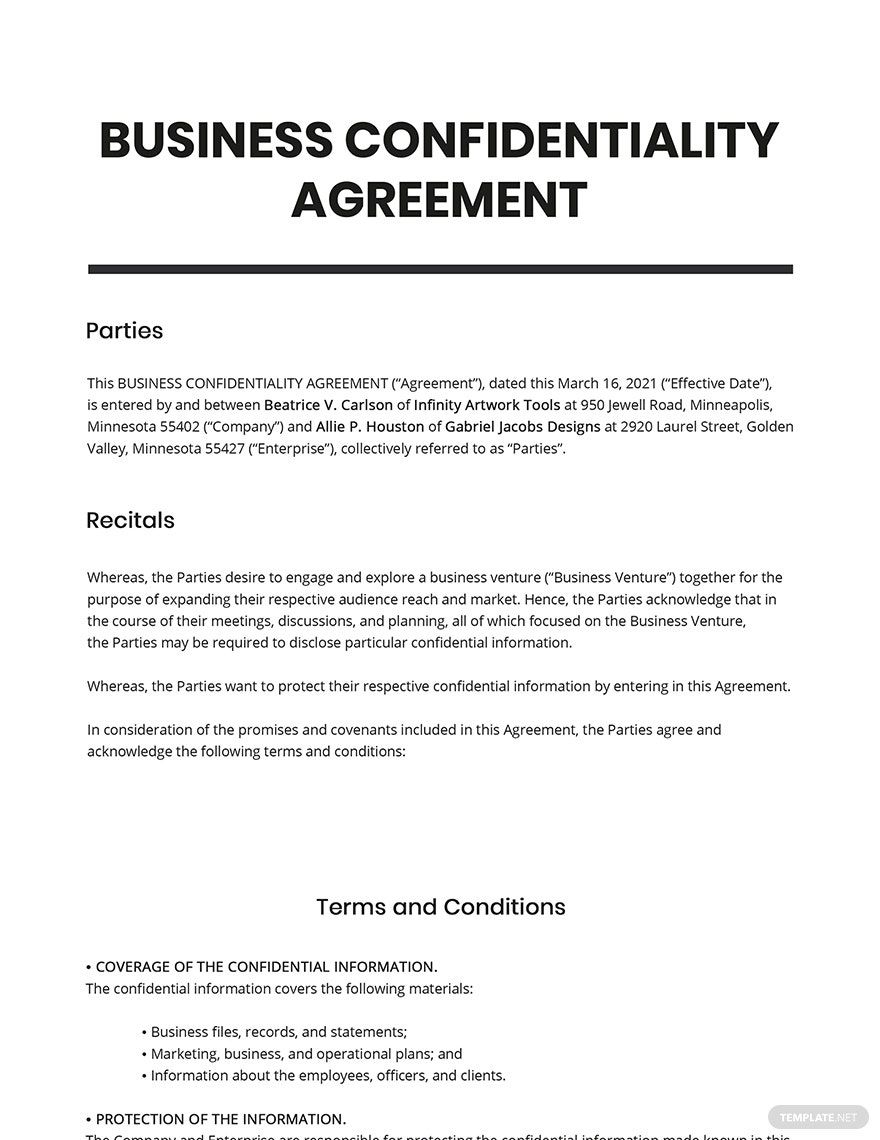
1. Definitions
This section defines key terms used throughout the agreement. It’s vital to ensure everyone involved understands the meaning of each term, preventing ambiguity and potential disputes. Examples include “Confidential Information,” “Recipient,” “Data Processor,” and “Authorized User.” A clear and precise definition of each term is essential.
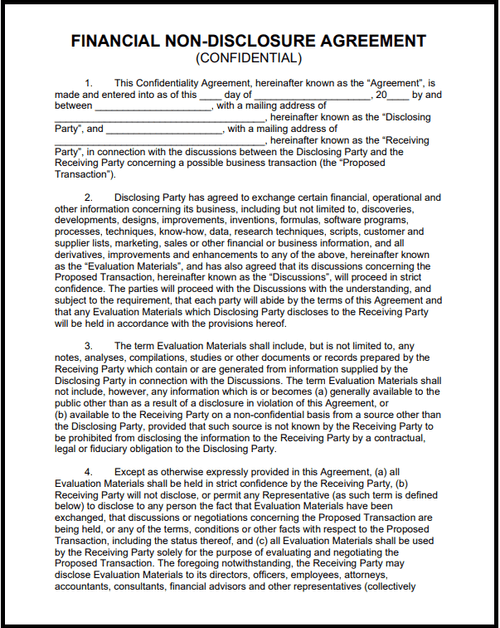
2. Scope of Confidentiality
This section explicitly states what information is covered by the FCA. It’s crucial to be specific about the types of data being protected. For example, it might include financial records, customer lists, product designs, and marketing plans. It’s important to avoid overly broad language that could inadvertently cover unintended information.
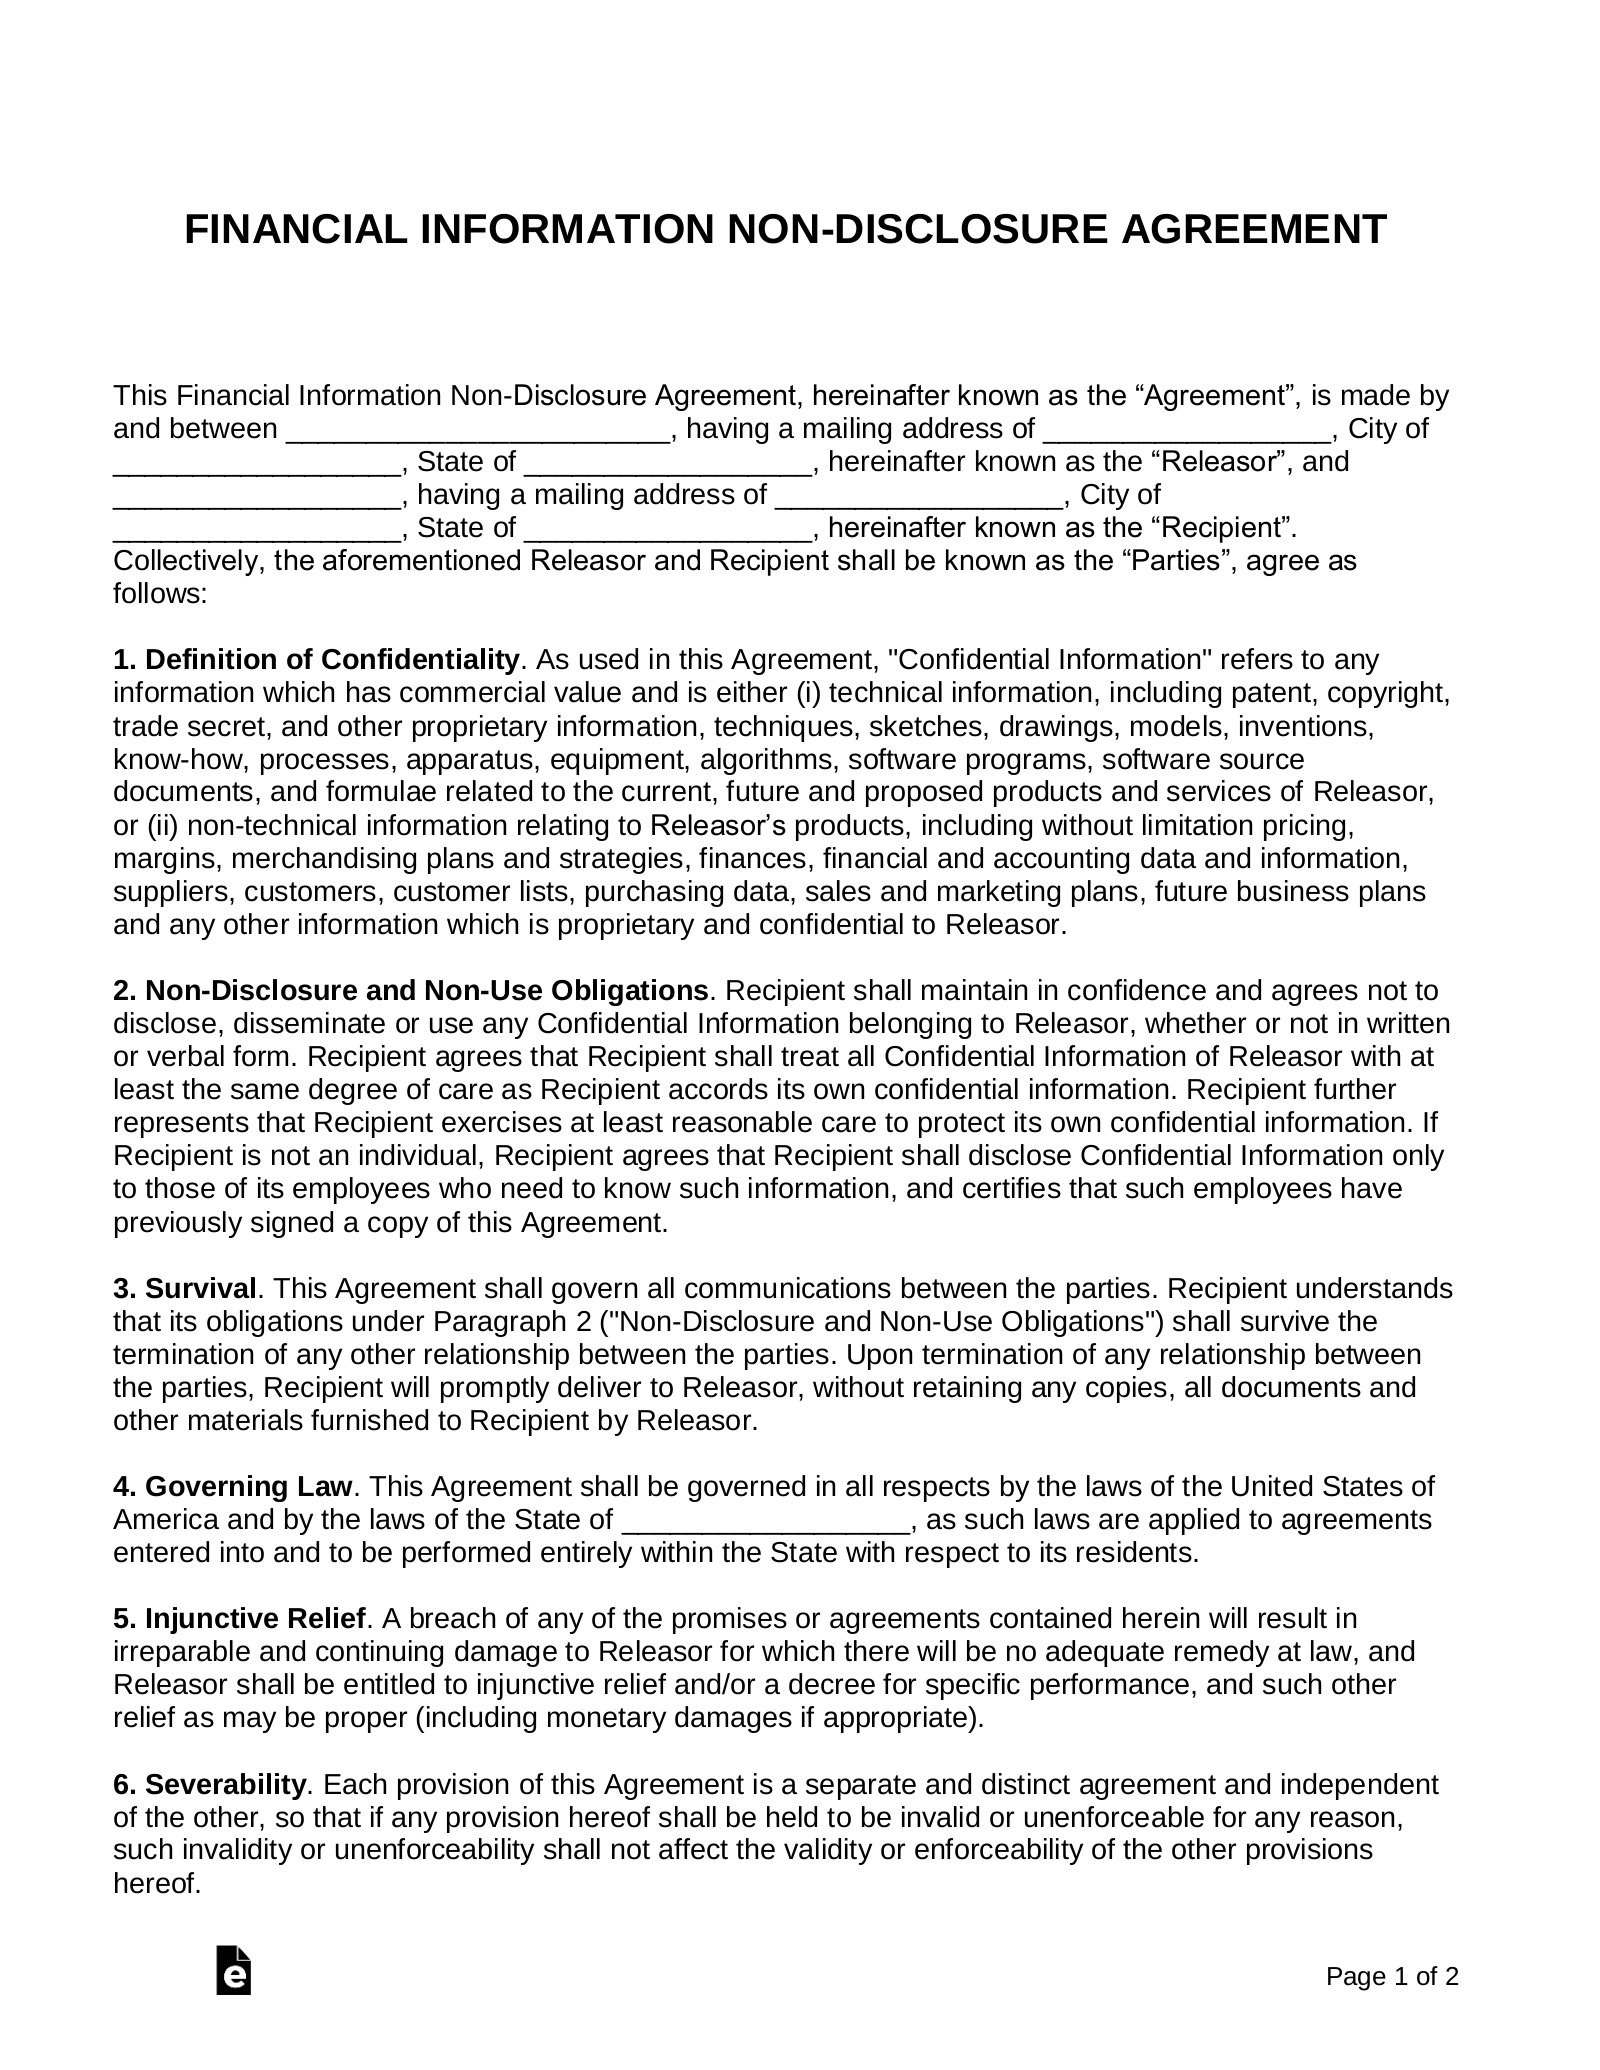
3. Permitted Uses of Confidential Information
This section details how the recipient can utilize the confidential information. It’s vital to limit the use to only those purposes explicitly authorized by both parties. For instance, a financial institution might allow a third-party marketing firm to use customer data for targeted advertising, but not to develop a competing product.
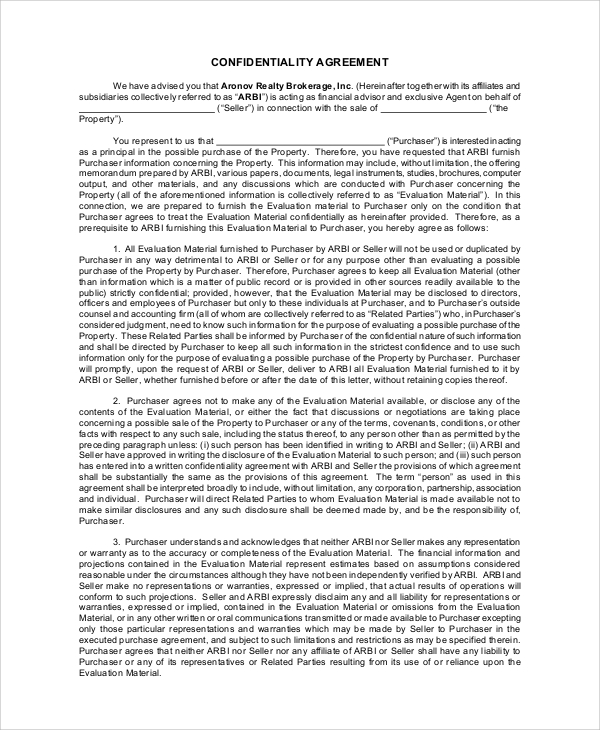
4. Data Security and Protection Measures
This section addresses the security measures the recipient is required to implement to protect the confidential information. This might include encryption, access controls, and data loss prevention (DLP) systems. It’s important to specify the level of security required and the recipient’s responsibility to maintain it. Consider including provisions for data backups and disaster recovery.
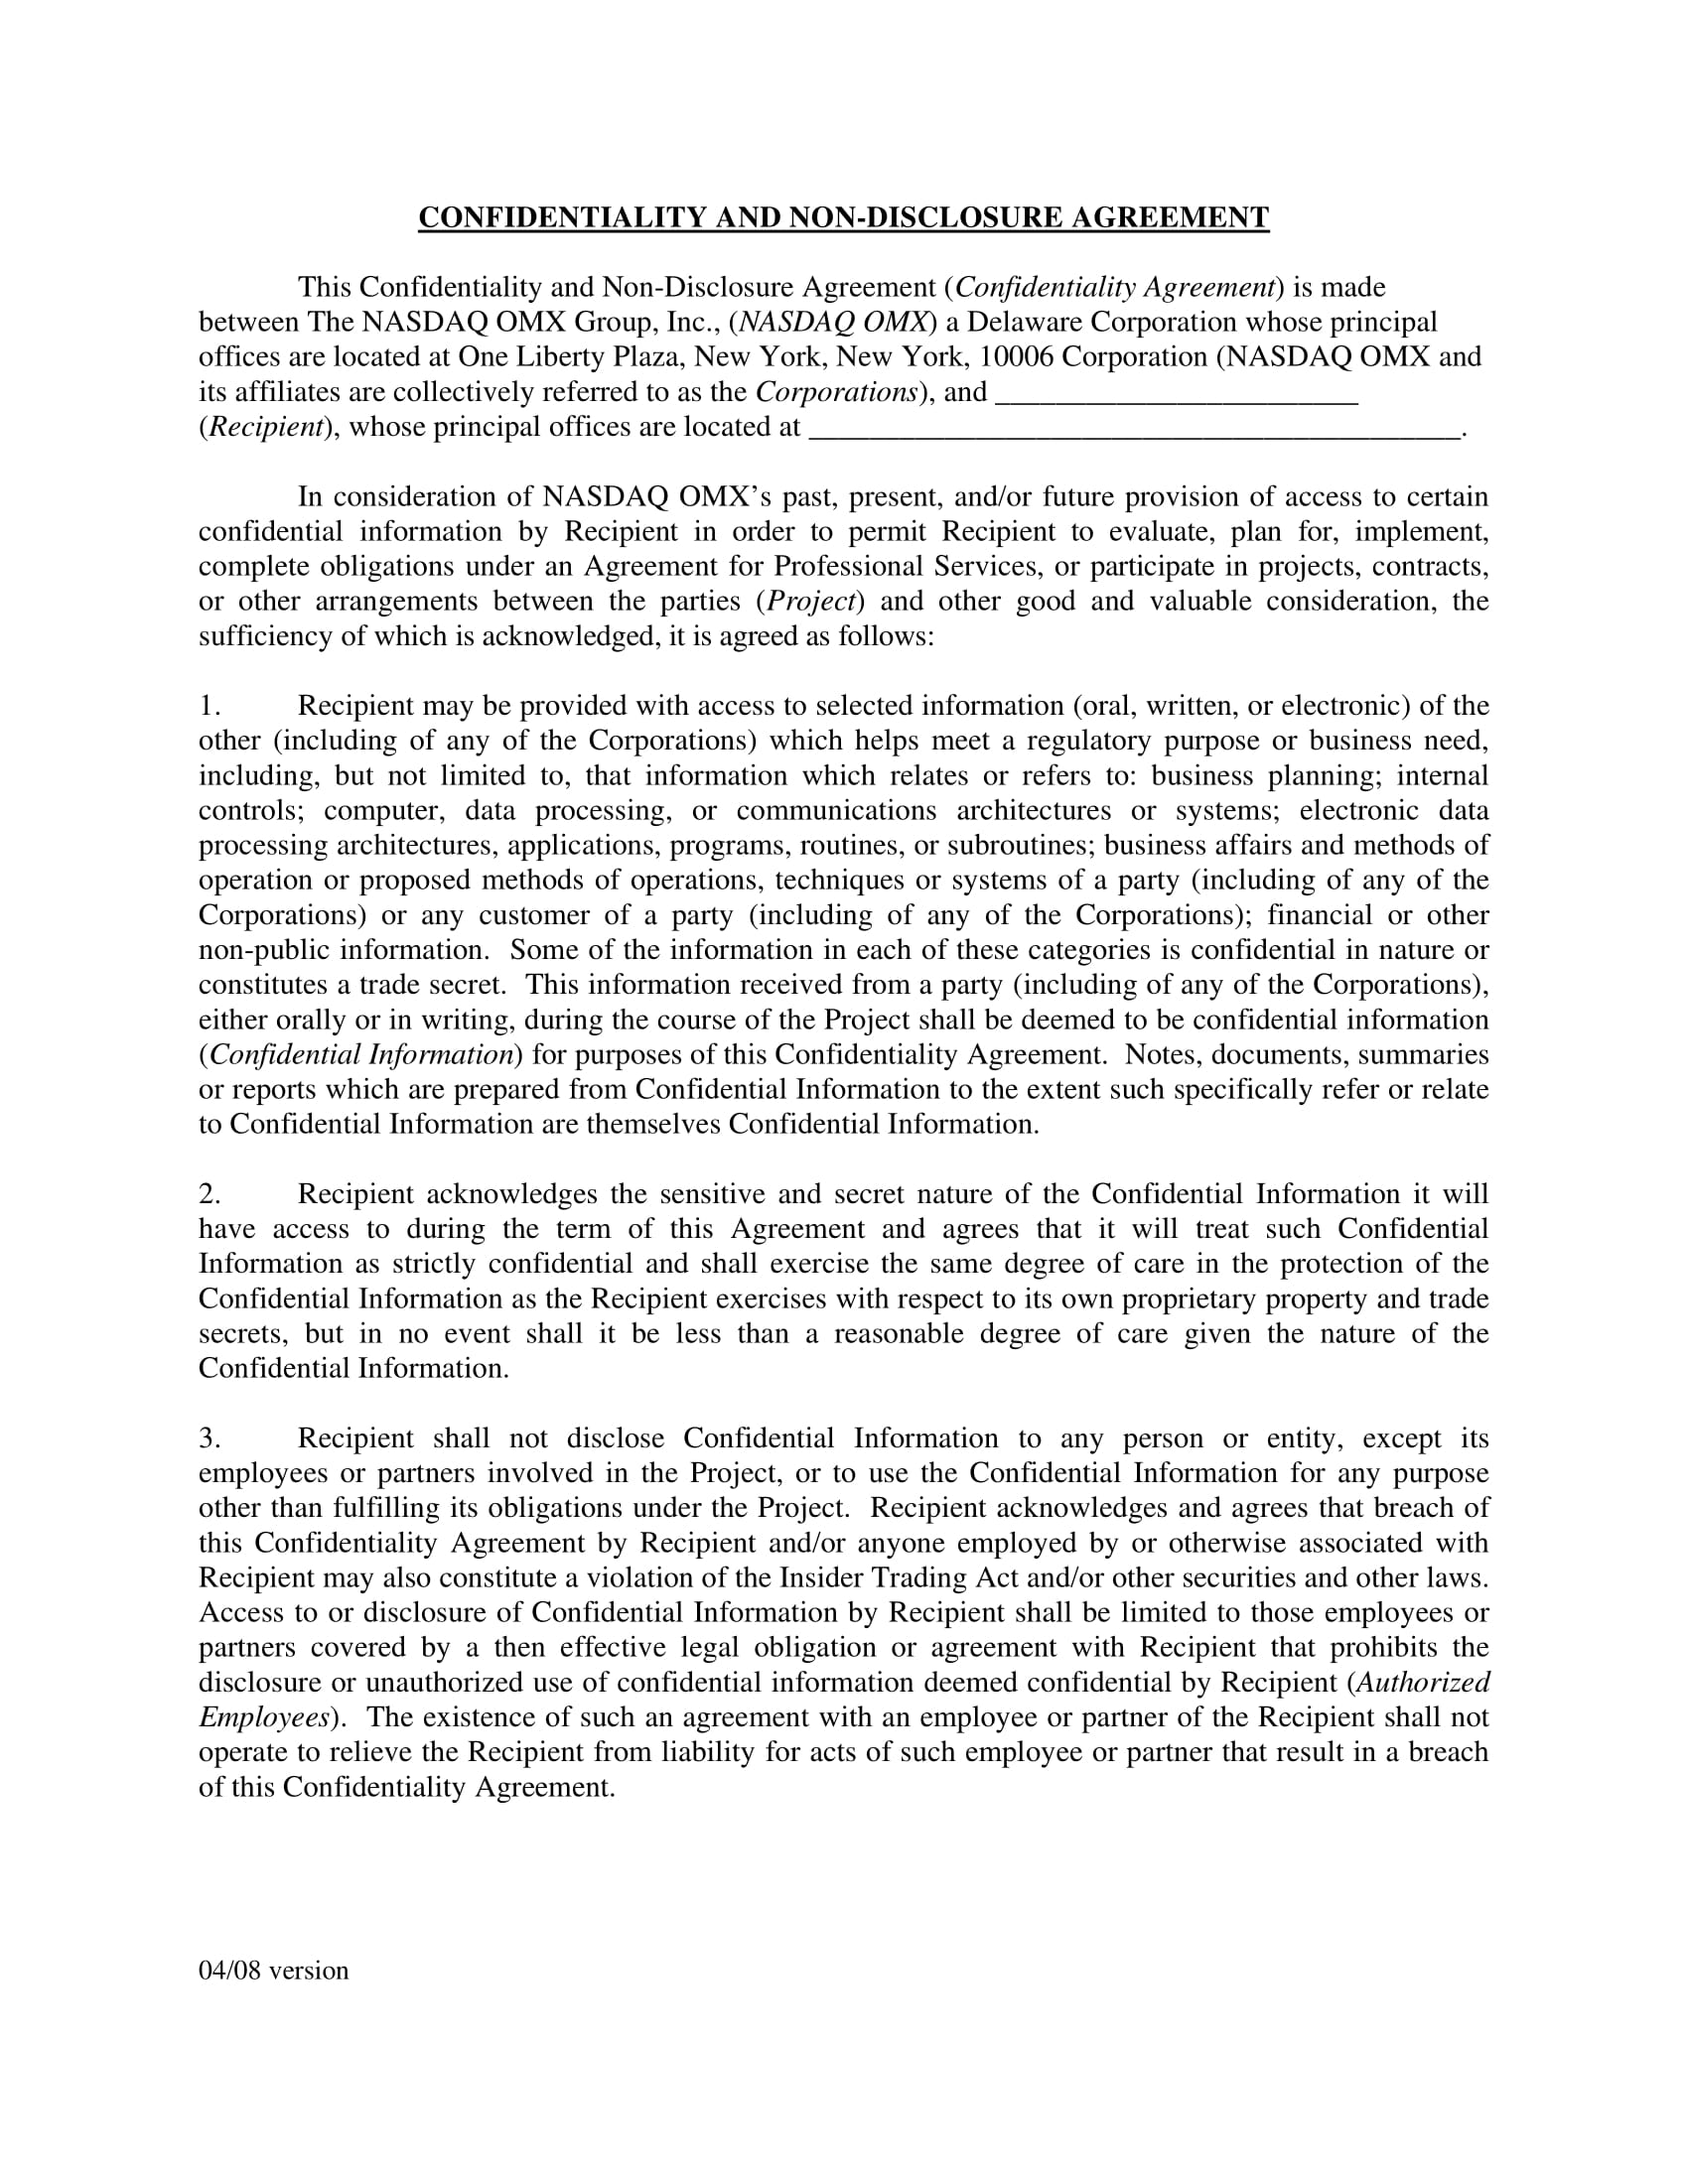
5. Data Retention Policy
This section outlines how long the recipient is permitted to retain the confidential information. It’s important to balance the need to protect confidential information with the need to comply with legal and regulatory requirements. The retention period should be reasonable and aligned with industry best practices.
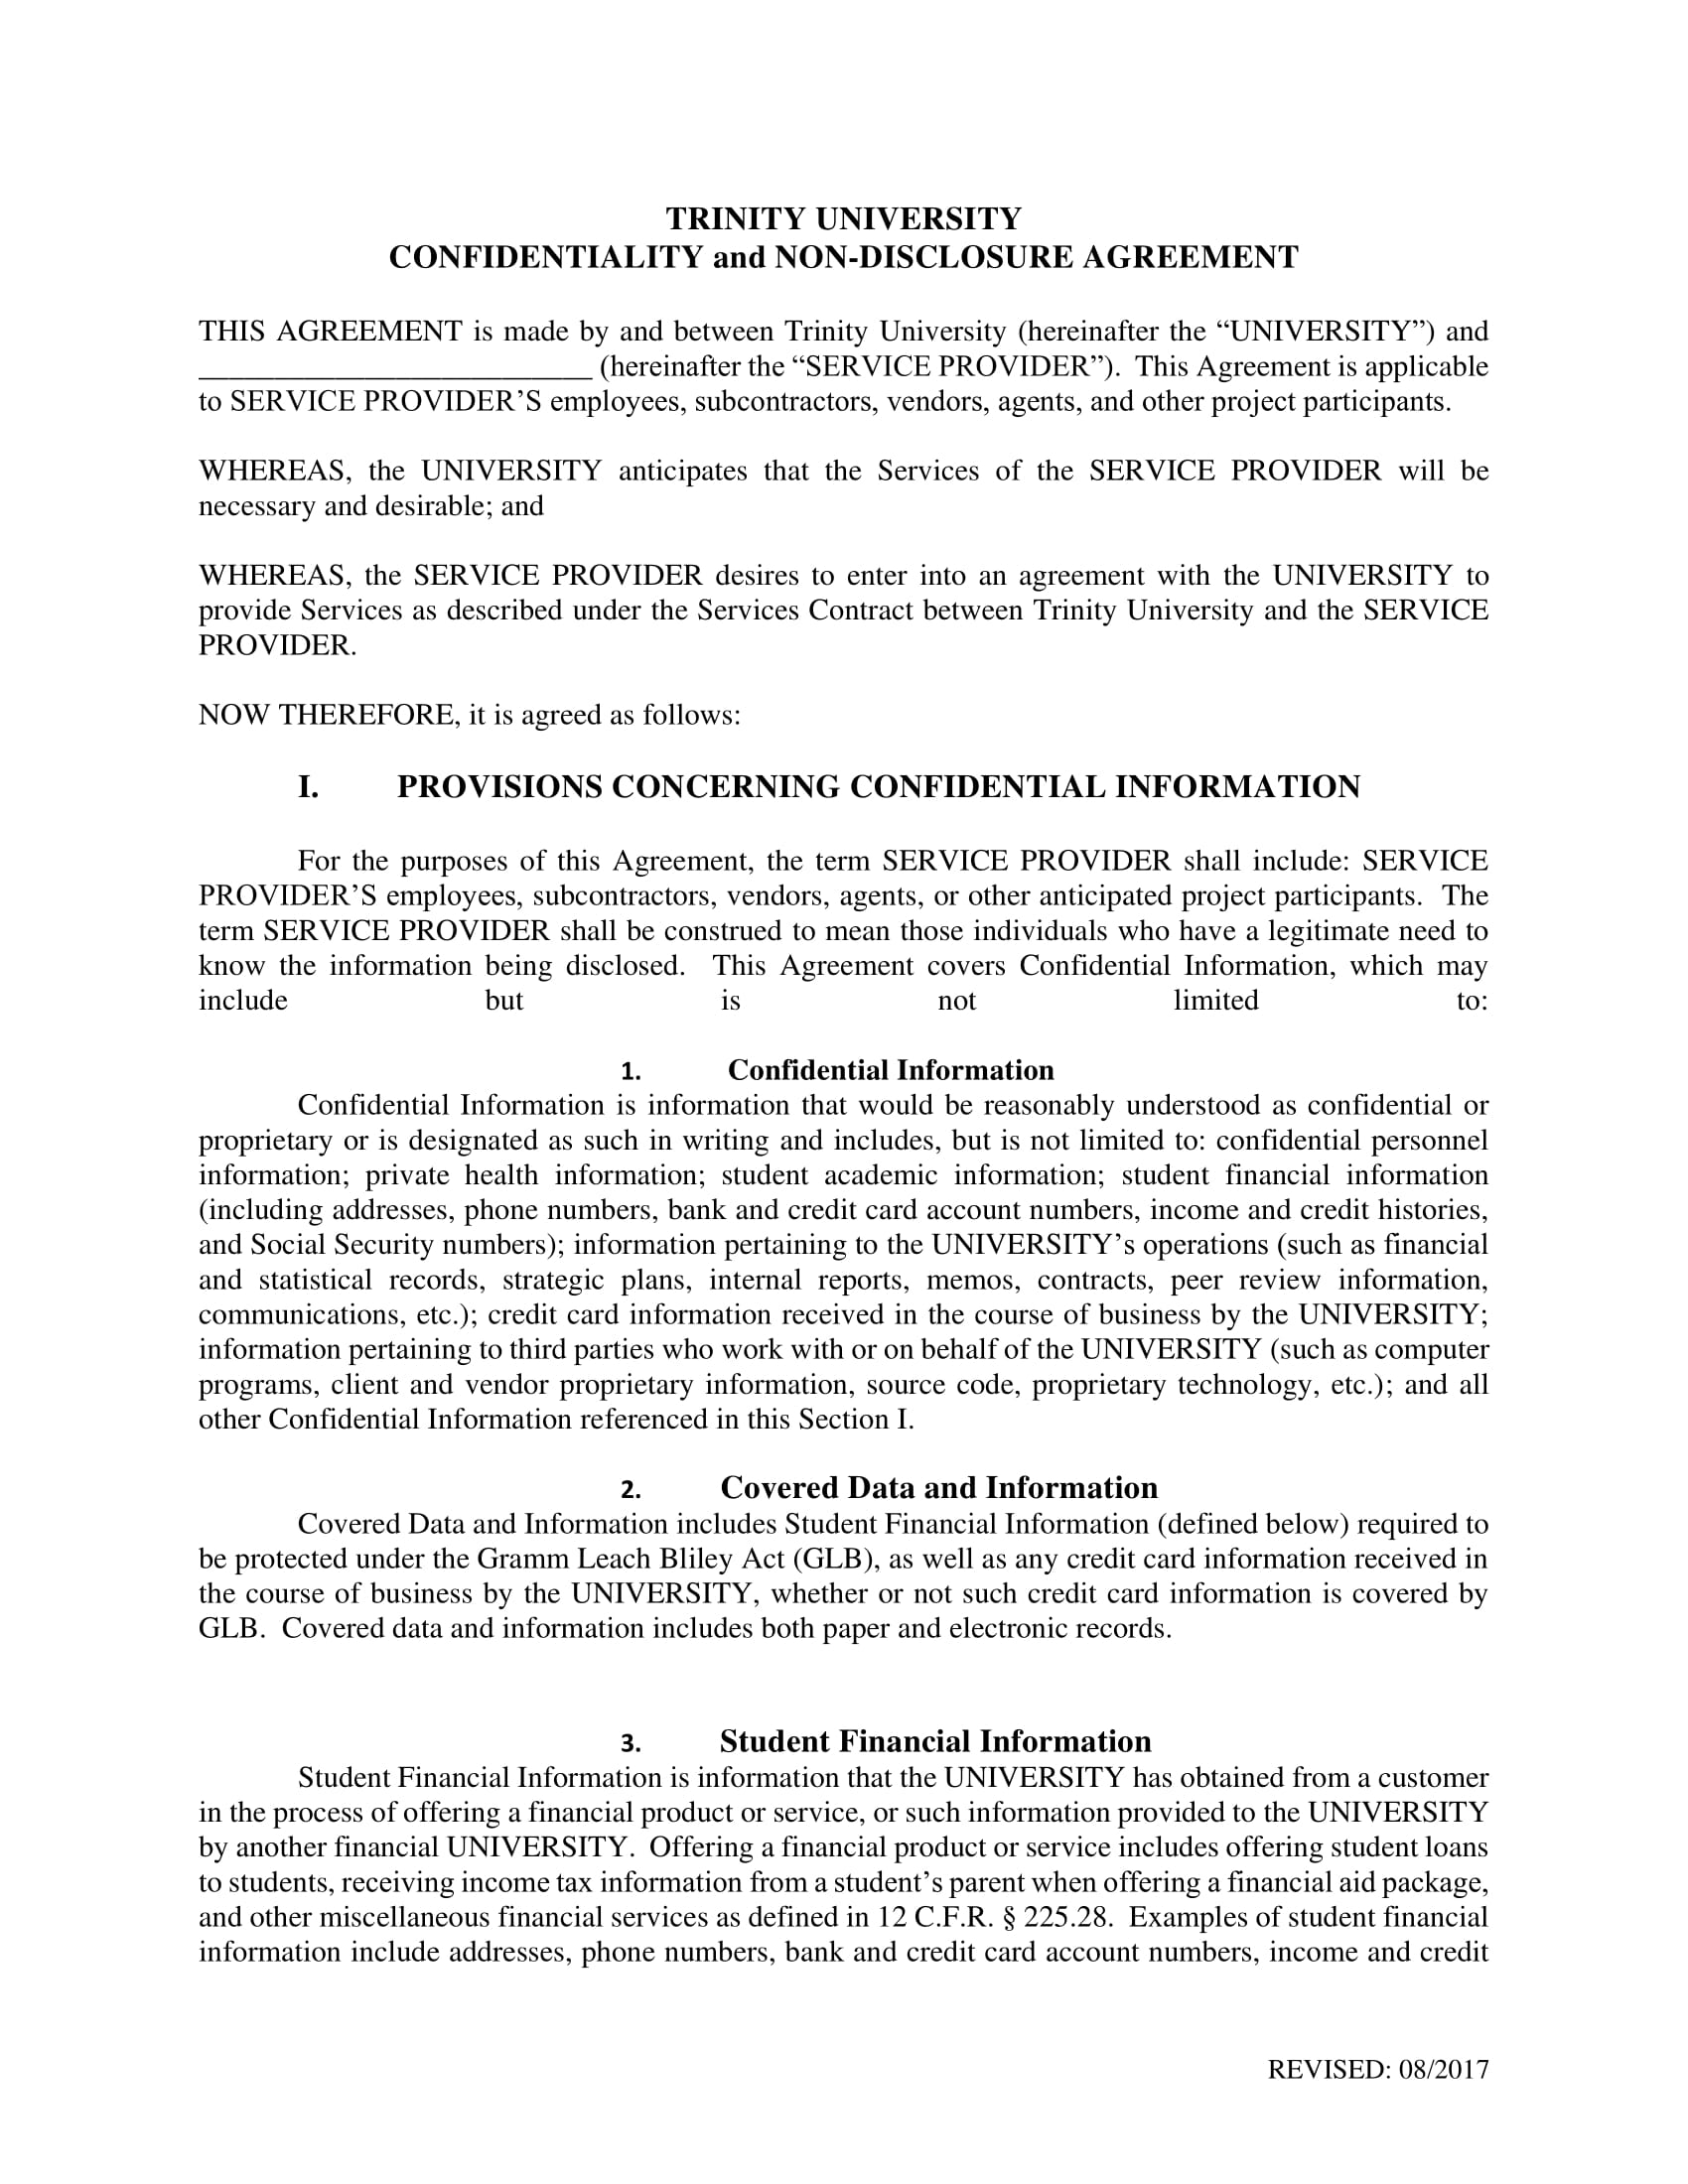
6. Breach Notification
This section outlines the procedures for reporting a breach of confidentiality. It should include contact information for the reporting party and a clear process for investigating and addressing the breach. Prompt notification is crucial to minimize damage.
7. Governing Law and Dispute Resolution
This section specifies the jurisdiction whose laws will govern the agreement and how disputes will be resolved (e.g., arbitration, mediation, or litigation). Clearly defined dispute resolution mechanisms can help avoid costly and time-consuming legal battles.
The Importance of a Tailored Agreement
While a standard FCA template provides a solid foundation, it’s crucial to tailor the agreement to the specific circumstances of each relationship. Factors to consider include the nature of the information being shared, the level of risk involved, and the regulatory environment. A one-size-fits-all approach is rarely effective. A consultation with legal counsel is highly recommended to ensure the FCA accurately reflects the specific needs of your organization.
Benefits of Implementing a Robust FCA
Investing in a well-crafted FCA offers numerous benefits:

- Reduced Legal Risk: Minimizes the risk of lawsuits and regulatory penalties.
- Enhanced Client Trust: Demonstrates a commitment to protecting sensitive information, fostering trust with clients.
- Improved Data Security: Encourages the recipient to implement appropriate security measures.
- Compliance with Regulations: Helps organizations comply with data privacy laws like GDPR and CCPA.
- Protection of Intellectual Property: Safeguards valuable trade secrets and proprietary information.
- Streamlined Business Operations: Reduces the potential for disputes and misunderstandings.
Best Practices for Drafting an Effective FCA
- Be Specific: Avoid vague language and clearly define all terms and conditions.
- Keep it Concise: While thorough, strive for clarity and avoid unnecessary jargon.
- Review and Update: Regularly review and update the FCA to reflect changes in the business environment and legal requirements.
- Seek Legal Counsel: Consult with an attorney specializing in data privacy and confidentiality agreements to ensure the FCA is legally sound and protects your organization’s interests.
- Document Everything: Maintain thorough records of the FCA and all communications related to its implementation.
Conclusion
A Financial Confidentiality Agreement is an indispensable tool for organizations operating in today’s data-driven world. By carefully considering the key components outlined in this article and tailoring the agreement to your specific needs, you can significantly reduce your risk of data breaches, protect your client relationships, and maintain a competitive advantage. Remember, proactive protection of confidential information is not just a legal obligation; it’s a fundamental aspect of responsible business practice. Financial Confidentiality Agreement Template – a vital document for safeguarding valuable assets and building a sustainable business.
Conclusion
Related posts of "Financial Confidentiality Agreement Template"
